

Microsoft MS-500 Premium Exam Engine pdf - Download Free Updated 231 Questions
Verified MS-500 Bundle Real Exam Dumps PDF
Most of those IT specialists who want to become Security Administrators or verify their knowledge by a popular certification vendor in this sector opt for Microsoft and its MS-500 exam. After passing this test, you will be awarded the Microsoft 365 Certified: Security Administrator Associate certificate, but before that, you need to prepare well and explore all the important details related to this qualifying exam.
Microsoft MS-500 and Skills Measured
To become a certified professional by passing the MS-500 exam, you need to prepare with great deliberation and try to master all the topics covered in the content. All in all, you will need to be ready for the following domains that will evaluate your skills:
- Implementation & Management of Access & Identity (30-35%)
This area is all about the implementation and security procedures that are required for the efficient and safe working process. The procedures are connected with the authentication methods, role-based access control, Microsoft 365 hybrid environments, identities, conditional access, Azure AD Identity Protection, and Azure AD Privileged Identity Management.
- Implementation & Management of Threat Protection (20-25%)
For this topic, you need to be able to implement threat protection for a device, Microsoft Defender for Office 365, enterprise hybrid threat protection solution, as well as device and application protection. The ability to monitor Microsoft 365 Security with Azure Sentinel is also important.
- Implementation of Information Protection & Its Management (15-20%)
The questions from this section will evaluate your skills in managing data loss prevention and sensitivity labels, implementing Microsoft Cloud App Security and managing it, as well as securing data access within Office 365.
- Management of Compliance & Governance Features in Microsoft 365 (25-30%)
The last objective teaches you how to manage data governance and retention, investigation and search, and data privacy regulation compliance. You should also know about the analysis of audit logs and reports and configuration of security reporting.
NEW QUESTION 73
注:この質問は同じシナリオを提示する一連の質問の一部です。の各質問
シリーズは述べられた目的を満たすかもしれないユニークな解決策を含みます。いくつかの質問セット
他の人が正しい解決策を持っていないかもしれない間、複数の正しい解決策を持っています。
このセクションで質問に答えた後は、それに戻ることはできません。その結果、
質問はレビュー画面に表示されません。
Microsoft Azure Active Directory(Azure)に関連付けられているMicrosoft 365 E5サブスクリプションがあります。
contoso.comという名前のAD)テナント。
Active Directoryフェデレーションサービス(AD FS)を使用して、オンプレミスのActive Directoryと
テナント。 Azure AD Connectには次の設定があります。
ソースアンカー:objectGUID
パスワードハッシュ同期:無効
パスワードライトバック:無効
ディレクトリ拡張属性の同期:無効
Azure ADアプリと属性のフィルタリング:無効
Exchangeハイブリッド展開:無効
ユーザライトバック:無効
Azure AD Identity Protectionで漏洩した資格情報の検出を使用できるようにする必要があります。
解決策:Azure ADアプリと属性フィルターの設定を変更します。
それは目標を達成していますか?
- A. いいえ
- B. はい
Answer: A
NEW QUESTION 74
You have a Microsoft 365 Enterprise E5 subscription.
You use Windows Defender Advanced Threat Protection (Windows Defender ATP). You plan to use
Microsoft Office 365 Attack simulator.
What is a prerequisite for running Attack simulator?
- A. Configure Advanced Threat Protection (ATP)
- B. Integrate Office 365 Threat Intelligence and Windows Defender ATP
- C. Create a Conditional Access App Control policy for accessing Office 365
- D. Enable multi-factor authentication (MFA)
Answer: D
Explanation:
Explanation/Reference:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/attack-simulator
NEW QUESTION 75
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION 76
Several users in your Microsoft 365 subscription report that they received an email message without the attachment. You need to review the attachments that were removed from the messages. Which two tools can you use? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A. the Security & Compliance admin center
- B. Microsoft Azure Security Center
- C. the Exchange admin center
- D. Outlook on the web
- E. the Azure ATP admin center
Answer: A,C
Explanation:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/manage-quarantined-messages-and-files
NEW QUESTION 77
You have a Microsoft 365 subscription.
You have a Microsoft SharePoint Online site named Site1. The files in Site1 are protected by using Microsoft Azure Information Protection.
From the Security & Compliance admin center, you create a label that designates personal data.
You need to auto-apply the new label to all the content in Site1.
What should you do first?
- A. Remove Azure Information Protection from the Site1 files.
- B. From PowerShell, run Set-ComplianceTag.
- C. From PowerShell, run Set-ManagedContentSettings.
- D. From the Security & Compliance admin center, create a Data Subject Request (DSR).
Answer: A
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/apply-labels-to-personal-data-in-office-365
NEW QUESTION 78
You need to ensure that a user named Grady Archie can monitor the service health of your Microsoft 365 tenant. The solution must use the principle of least privilege.
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to assign the Service Administrator role to Grady Archie.
* In the Microsoft 365 Admin Center, type Grady Archie into the Search for users, groups, settings or tasks search box.
* Select the Grady Archie user account from the search results.
* In the Roles section of the user account properties, click the Edit link.
* Select the Customized Administrator option. This will display a list of admin roles.
* Select the Service admin role.
* Click Save to save the changes.
NEW QUESTION 79
Note: This question is part of a series of questions thatpresent the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some questions sets might have more than one correct solution, while others might not have a correct solution.
After you answer a questionin this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommendremoving User1 from the Compliance Manager Contributor role.
Does that meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/working-with-compliance-manager
NEW QUESTION 80
Note: This question is part of series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 E5 subscription that is associated to a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
You use Active Directory Federation Services (AD FS) to federate on-premises Active Directory and the tenant.
Azure AD Connect has the following settings:
* Source Anchor: objectGUID
* Password Hash Synchronization: Disabled
* Password writeback: Disabled
* Directory extension attribute sync: Disabled
* Azure AD app and attribute filtering: Disabled
* Exchange hybrid deployment: Disabled
* User writeback: Disabled
You need to ensure that you can use leaked credentials detection in Azure AD Identity Protection.
Solution: You modify the Azure AD app and attribute filtering settings.
Does that meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 81
You have a Microsoft 365 subscription that uses a default domain name of contoso.com.
The multi-factor authentication (MFA) service settings are configured as shown in the exhibit. (Clock the Exhibit tab.)
In contoso.com, you create the users shown in the following table.
What is the effect of the configuration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: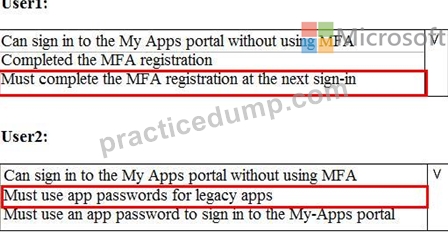
NEW QUESTION 82
You install Azure ATP sensors on domain controllers.
You add a member to the Domain Admins group. You view the timeline in Azure ATP and discover that information regarding the membership change is missing.
You need to meet the security requirements for Azure ATP reporting.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/atp-advanced-audit-policy
NEW QUESTION 83
You have a Microsoft 365 subscription.
You create a retention label named Label1 as shown in the following exhibit.
You publish Label1 to SharePoint sites.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/labels
NEW QUESTION 84
You have a Microsoft 365 E5 subscription.
All computers run Windows 10 and are onboarded to Windows Defender Advanced Threat Protection (Windows Defender ATP).
You create a Windows Defender machine group named MachineGroupl.
You need to enable delegation for the security settings of the computers in MachineGroupl.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - From the Microsoft Azure portal, create an Azure Active Directory (Azure AD) group.
2 - From Windows Defender Security Center, create a role.
3 - From Windows Defender Security Center,configure the permissions for MachineGroup1.
NEW QUESTION 85
You have a Microsoft 365 E5 subscription.
All computers run Windows 10 and are onboarded to Windows Defender Advanced Threat Protection (Windows Defender ATP).
You create a Windows Defender machine group named MachineGroupl.
You need to enable delegation for the security settings of the computers in MachineGroupl.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.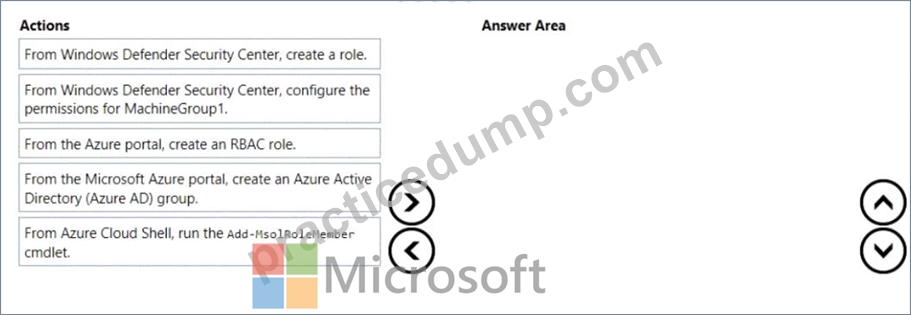
Answer:
Explanation:
Explanation
NEW QUESTION 86
You need to configure threat detection for Active Directory. The solution must meet the security requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: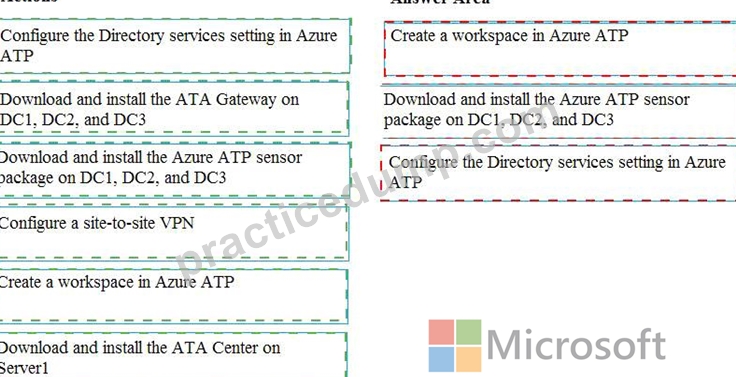
Explanation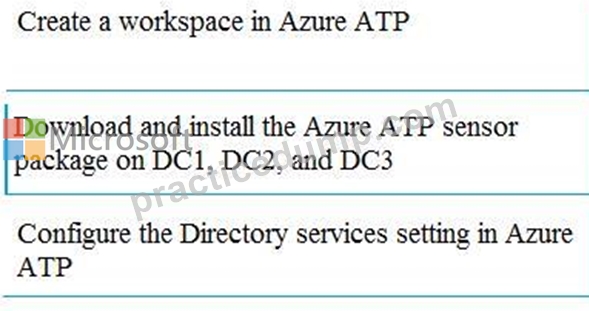
NEW QUESTION 87
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You plan to implement Azure Active Directory (Azure AD) Identity Protection.
You need to identify which users can perform the following actions:
* Configure a user risk policy.
* View the risky users report.
Which users should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/overview-identity-protection
NEW QUESTION 88
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION 89
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308


You need to ensure that a user named Allan Deyoung can perform searches and place holds on mailboxes, SharePoint Online sites, and OneDrive for Business locations. The solution must use the principle of least privilege.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
* After signing in to the Microsoft 365 admin center, navigate to the Security & Compliance Center.
* In the left pane of the security and compliance center, select Permissions, and then select the checkbox next to eDiscovery Manager.
* On the eDiscovery Manager flyout page, do one of the following based on the eDiscovery permissions that you want to assign.
To make a user an eDiscovery Manager: Next to eDiscovery Manager, select Edit. In the Choose eDiscovery Manager section, select the Choose eDiscovery Manager hyperlink, and then select + Add.
Select the user (or users) you want to add as an eDiscovery manager, and then select Add. When you're finished adding users, select Done. Then, on the Editing Choose eDiscovery Manager flyout page, select Save to save the changes to the eDiscovery Manager membership.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/assign-ediscovery-permissions?view=o365-worldwi
NEW QUESTION 90
You have a Microsoft 365 subscription that uses an Azure Active Directory (Azure AD) tenant named contoso.com. OneDrive stores files that are shared with external users. The files are configured as shown in the following table.
You create a data loss prevention (DLP) policy that applies to the content stored in OneDrive accounts. The policy contains the following three rules:
* Rulel:
* Conditions: Label 1, Detect content that's shared with people outside my organization
* Actions: Restrict access to the content for external users
* User notifications: Notify the user who last modified the content
* User overrides: On
* Priority: 0
* Rule2:
* Conditions: Label 1 or Label2
* Actions: Restrict access to the content
* Priority: 1
* Rule3:
* Conditions: Label2, Detect content that's shared with people outside my organization
* Actions: Restrict access to the content for external users
* User notifications: Notify the user who last modified the content
* User overrides: On
* Priority: 2
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 91
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) willnot be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are nottimed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enteryour username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft365 Password:#HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance:11122308


You need to ensure that all the email messages in the mailbox of a user named Allan Deyoung are retained for a period of 90 days, even if the messages are deleted.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
1. Navigate to theExchange Admin Center
2. Navigate toCompliance management>Retention tags, and then clickAdd+
3. Select theApplied automatically to entire mailbox (default)option.
4. TheNew retention tagpage title and options will vary depending on the type of tag you selected. Complete the following fields:
Name: Enter a name for the retention tag.
Retention action: SelectDelete and Allow Recoveryoption.
Retention period: SelectWhen the item reachesthe following age (in days)option.
Comment: User this optional field to enter any administrative notes or comments. The field isn't displayed to users.
5. Navigate toCompliance management>Retention policies, and then clickAdd+
6. InNew Retention Policy, complete the following fields:
Name: Enter a name for the retention policy.
Retention tags: ClickAdd+to select the tags you want to add to this retention policy.
After you create a retention policy, you must apply it.
1. Navigate toRecipients>Mailboxes
2. In the list view, select the mailbox to which you want to apply the retention policy, and then clickEdit.
3. InUser Mailbox, clickMailbox features
4. In theRetention policylist, select the policy you want to apply to the mailbox, and then clickSave.
Reference:
https://docs.microsoft.com/en-us/exchange/security-and-compliance/messaging-records-management/create-a-r
https://docs.microsoft.com/en-us/exchange/security-and-compliance/messaging-records-management/apply-rete
NEW QUESTION 92
You have a Microsoft 365 subscription.
A customer requests that you provide her with all documents that reference her by name.
You need to provide the customer with a copy of the content.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/gdpr-dsr-office365
NEW QUESTION 93
Which policies apply to which devices? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 94
You need to configure threat detection for Active Directory. The solution must meet the security requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Topic 2, Fabrikam inc.
Overview
Fabrikam, Inc. is manufacturing company that sells products through partner retail stores. Fabrikam has 5,000 employees located in offices throughout Europe.
Existing Environment
Network Infrastructure
The network contains an Active Directory forest named fabrikam.com. Fabrikam has a hybrid Microsoft Azure Active Directory (Azure AD) environment.
The company maintains some on-premises servers for specific applications, but most end-user applications are provided by a Microsoft 365 E5 subscription.
Problem Statements
Fabrikam identifies the following issues:
* Since last Friday, the IT team has been receiving automated email messages that contain "Unhealthy Identity Synchronization Notification" in the subject line.
* Several users recently opened email attachments that contained malware. The process to remove the malware was time consuming.
Requirements
Planned Changes
Fabrikam plans to implement the following changes:
* Fabrikam plans to monitor and investigate suspicious sign-ins to Active Directory
* Fabrikam plans to provide partners with access to some of the data stored in Microsoft 365 Application Administration Fabrikam identifies the following application requirements for managing workload applications:
* User administrators will work from different countries
* User administrators will use the Azure Active Directory admin center
* Two new administrators named Admin1 and Admin2 will be responsible for managing Microsoft Exchange Online only Security Requirements Fabrikam identifies the following security requirements:
* Access to the Azure Active Directory admin center by the user administrators must be reviewed every seven days. If an administrator fails to respond to an access request within three days, access must be removed
* Users who manage Microsoft 365 workloads must only be allowed to perform administrative tasks for up to three hours at a time. Global administrators must be exempt from this requirement
* Users must be prevented from inviting external users to view company data. Only global administrators and a user named User1 must be able to send invitations
* Azure Advanced Threat Protection (ATP) must capture security group modifications for sensitive groups, such as Domain Admins in Active Directory
* Workload administrators must use multi-factor authentication (MFA) when signing in from an anonymous or an unfamiliar location
* The location of the user administrators must be audited when the administrators authenticate to Azure AD
* Email messages that include attachments containing malware must be delivered without the attachment
* The principle of least privilege must be used whenever possible
NEW QUESTION 95
You have several Conditional Access policies that block noncompliant devices from connecting to services.
You need to identity which devices are blocked by which policies.
What should you use?
- A. the Setting compliance report in the Microsoft Endpoint Manager admin center
- B. Activity log in the Cloud App Security admin center
- C. Sign-ins in the Azure Active Directory admin center
- D. Audit logs in the Azure Active Directory admin center
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/troubleshoot-conditional-access
NEW QUESTION 96
......
For more info visit:
Microsoft MS-500 Exam Reference
Pass Your Microsoft Exam with MS-500 Exam Dumps: https://www.practicedump.com/MS-500_actualtests.html
MS-500 Dumps PDF New [2021] Ultimate Study Guide: https://drive.google.com/open?id=18uS0CnRrFC2PBUSqImiVRgE-N9TOqK8X