

[2025] Practice with these 300-730 dumps Certification Sample Questions
Get Instant Access of 100% REAL 300-730 DUMP Pass Your Exam Easily
Cisco 300-730 certification exam consists of 60-70 multiple-choice and simulation questions. 300-730 exam duration is 90 minutes. The passing score for the exam is 70%. 300-730 exam is available in English and Japanese languages. 300-730 exam fee is $300 USD.
NEW QUESTION # 41
After a user configures a connection profile with a bookmark list and tests the clientless SSLVPN connection, all of the bookmarks are grayed out. What must be done to correct this behavior?
- A. Configure a DNS server on the Cisco ASA and verify it has a record for the web server.
- B. Verify HTTP/HTTPS connectivity between the Cisco ASA and the web server.
- C. Specify the correct port for the web server under the bookmark.
- D. Apply the bookmark to the correct group policy.
Answer: A
NEW QUESTION # 42
Refer to the exhibit. A network engineer is troubleshooting a new DMVPN configuration. The network connectivity between the hub and spoke is working as it should, but users cannot access VPN resources. Which action resolves the issue?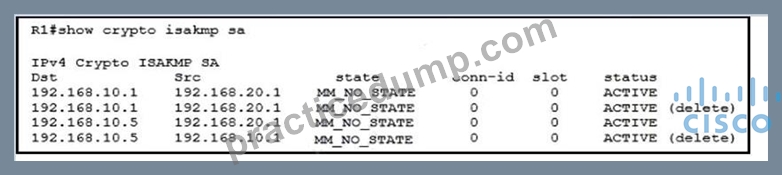
- A. Unblock IP protocol 50 on devices between the VPN devices.
- B. Review ISAKMP packets on devices between the VPN devices.
- C. Ensure that the NHS is configured on the tunnel interface.
- D. Ensure that the IPsec profile is configured on the tunnel interface.
Answer: D
Explanation:
The output of show crypto isakmp sa shows that all security associations are in the
"MM_NO_STATE" state. This indicates that IKE Phase 1 negotiation did not complete successfully, preventing IPsec tunnel establishment. A common cause of this issue in DMVPN (Dynamic Multipoint VPN) is that the IPsec profile is missing or incorrectly applied on the tunnel interface.
NEW QUESTION # 43
An engineer is implementing a failover solution for a FlexVPN client site where ESP traffic to the primary FlexVPN server is blocked intermittently after tunnel establishment. This issue causes users at the branch site to lose access to the corporate network. The solution must quickly establish a tunnel and send traffic to the secondary FlexVPN server only during a failover event.
Which action must the engineer take to implement this solution?
- A. Create one tunnel with peer statements to each server and use Dead Peer Detection to track the status or the primary server.
- B. Create two tunnels for each FlexVPN server and use a dynamic routing protocol to track the status or each FlexVPN server.
- C. Create one tunnel with peer statements to each server and use object tracking to track the status of the primary server.
- D. Create two tunnels for each FlexVPN server and use the tunnel keepalive command to track the status of each FlexVPN server.
Answer: A
NEW QUESTION # 44
Two VPN clients have established SSL VPN connections to the outside interface on same Cisco Secure Firewall ASA, but they cannot communicate with each other. Which CLI command must be entered on the Cisco Secure Firewall ASA to enable this communication?
- A. sysopt connection permit-vpn
- B. no nat-control
- C. same-security-traffic permit inter-interface
- D. same-security-traffic permit intra-interface
Answer: D
Explanation:
By default, Cisco Secure Firewall ASA does not allow traffic to pass between two VPN clients connected to the same interface (e.g., the outside interface for SSL VPN).
To allow communication between these VPN clients, you need to enable intra-interface traffic using the following command:
same-security-traffic permit intra-interface
This allows traffic to hairpin (U-turn) on the same interface, enabling VPN-to-VPN communication.
NEW QUESTION # 45
Which Diffie Hellman group should be used when ECDH is required in a VPN configuration?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
NEW QUESTION # 46
A network engineer must implement an SSLVPN Cisco AnyConnect solution that supports 500 concurrent users, ensures all traffic from the client passes through the ASA, and allows users to access all devices on the inside interface subnet (192.168.0.0/24). Assuming all other configuration is set up appropriately, which configuration implements this solution?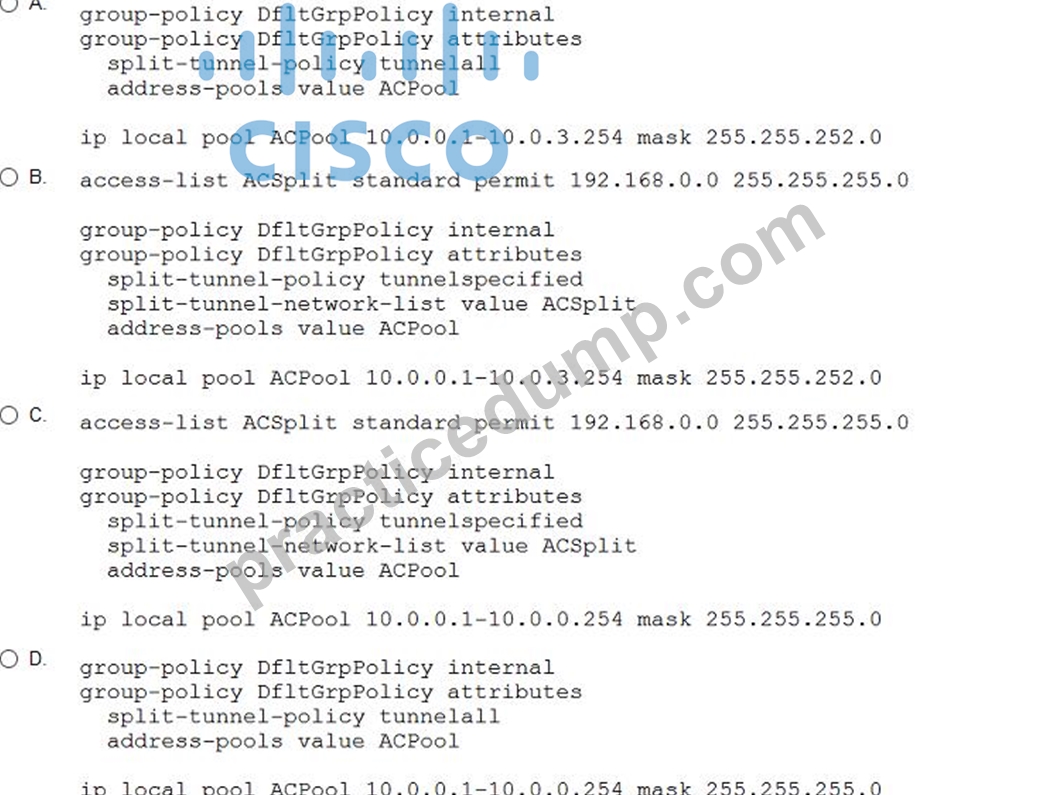
- A. Option B
- B. Option C
- C. Option A
- D. Option D
Answer: C
NEW QUESTION # 47 
Refer to the exhibit. A customer cannot establish an IKEv2 site-to-site VPN tunnel between two Cisco ASA devices. Based on the syslog message, which action brings up the VPN tunnel?
- A. Correct the crypto access list on both Cisco ASA devices.
- B. Reduce the maximum SA limit on the local Cisco ASA.
- C. Remove the maximum SA limit on the remote Cisco ASA.
- D. Increase the maximum in-negotiation SA limit on the local Cisco ASA.
Answer: D
Explanation:
Section: Site-to-site Virtual Private Networks on Routers and Firewalls
NEW QUESTION # 48
A network engineer must configure the Cisco ASA so that Cisco AnyConnect clients establishing an SSL VPN connection create an additional tunnel for real-time traffic that is sensitive to packet delays. If this additional tunnel experiences any issues, it must fall back to a TLS connection. Which two Cisco AnyConnect features must be configured to accomplish this task? (Choose two.)
- A. DPD
- B. SSL Rekey
- C. DSCP Preservation
- D. DTLS
- E. OMTU
Answer: A,D
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa96/configuration/vpn/asa-96-vpn-config/vpn-anyconnect.html Configure Dead Peer Detection Dead Peer Detection (DPD) ensures that the ASA (gateway) or the client can quickly detect a condition where the peer is not responding, and the connection has failed. To enable dead peer detection (DPD) and set the frequency with which either the AnyConnect client or the ASA gateway performs DPD, do the following: Before you begin This feature applies to connectivity between the ASA gateway and the AnyConnect SSL VPN Client only. It does not work with IPsec since DPD is based on the standards implementation that does not allow padding, and CLientless SSL VPN is not supported. If you enable DTLS, enable Dead Peer Detection (DPD) also. DPD enables a failed DTLS connection to fallback to TLS. Otherwise, the connection terminates.
NEW QUESTION # 49
A Cisco AnyConnect client establishes a SSL VPN connection with an ASA at the corporate office. An engineer must ensure that the client computer meets the enterprise security policy. Which feature can update the client to meet an enterprise security policy?
- A. Endpoint Assessment
- B. Cisco Secure Desktop
- C. Basic Host Scan
- D. Advanced Endpoint Assessment
Answer: D
NEW QUESTION # 50
Refer to the exhibit. The customer must launch Cisco AnyConnect in the RDP machine. Which IOS configuration accomplishes this task?
- A.

- B.

- C.

- D.

Answer: B
Explanation:
https://community.cisco.com/t5/vpn/starting-anyconnect-vpn-through-rdp-session-on-cisco-
891/td-p/2128284
NEW QUESTION # 51
Refer to the exhibit.
Cisco AnyConnect must be set up on a router to allow users to access internal servers 192.168.0.10 and 192.168.0.11. All other traffic should go out of the client's local NIC. Which command accomplishes this configuration?
- A. svc split include 192.168.0.0 255.255.255.0
- B. svc split exclude 192.168.0.0 255.255.255.0
- C. svc split exclude acl CCNP
- D. svc split include acl CCNP
Answer: D
NEW QUESTION # 52
An engineer must investigate a connectivity issue and decides to use the packet capture feature on Cisco FTD. The goal is to see the real packet going through the Cisco FTD device and see Snort detection actions as a part of the output. After the capture-traffic command is issued, only the packets are displayed. Which action resolves this issue?
- A. Use the verbose option as a part of the capture-traffic command
- B. Specify the trace using the -T option after the capture-traffic command
- C. Perform the trace within the Cisco FMC GUI instead of the Cisco FMC CLI
- D. Use the capture command and specify the trace option to get the required information
Answer: B
Explanation:
According to the document Use Firepower Threat Defense Captures and Packet Tracer, the capture- traffic command allows you to capture packets on the Snort engine domain of the FTD device. However, by default, it only shows the packet headers and does not include the Snort detection actions. To see the Snort detection actions, you need to use the -T option, which enables tracing.
NEW QUESTION # 53
Refer to the exhibit. Which action is demonstrated by this debug output?
- A. IPsec ISAKMP phase 1 negotiation.
- B. Disabling of the DMVPN tunnel interface.
- C. NHRP registration acknowledgement by the hub.
- D. NHRP initial registration by a spoke.
Answer: D
NEW QUESTION # 54
Which two NHRP functions are specific to DMVPN Phase 3 implementation? (Choose two.)
- A. resolution request
- B. redirect
- C. registration reply
- D. resolution reply
- E. registration request
Answer: A,E
Explanation:
Registration request is used by spoke routers to send a registration request to the hub router. The registration request includes the IP address of the spoke router and the protocol information. The hub router then sends a registration reply, which includes the IP address of the hub router.
Resolution request is used by spoke routers to send a resolution request to the hub router. The resolution request includes the IP address of the destination router. The hub router then sends a resolution reply, which includes the IP address of the destination router.
NEW QUESTION # 55
Refer to the exhibit.
A customer cannot establish an IKEv2 site-to-site VPN tunnel between two Cisco ASA devices. Based on the syslog message, which action brings up the VPN tunnel?
- A. Correct the crypto access list on both Cisco ASA devices.
- B. Reduce the maximum SA limit on the local Cisco ASA.
- C. Remove the maximum SA limit on the remote Cisco ASA.
- D. Increase the maximum in-negotiation SA limit on the local Cisco ASA.
Answer: D
NEW QUESTION # 56
Refer to the exhibit.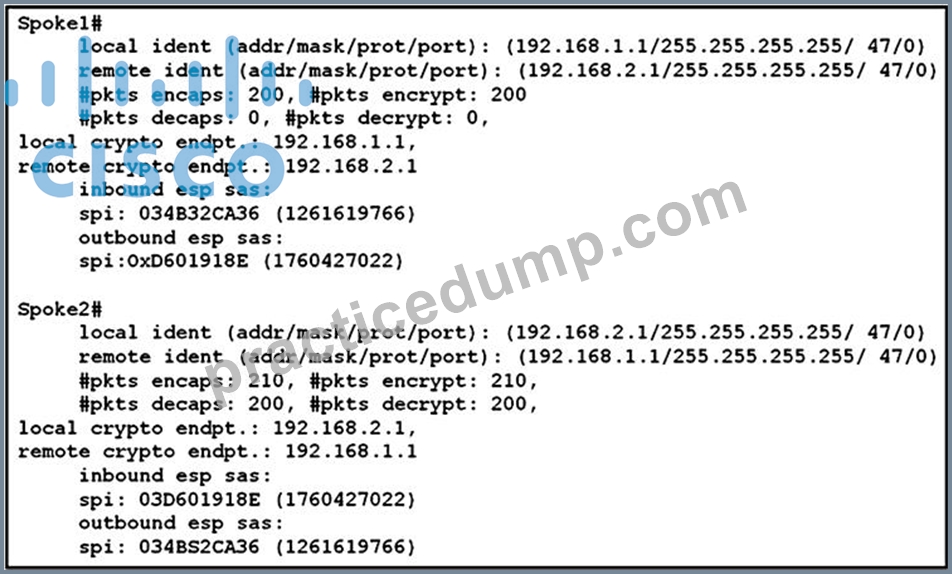
An engineer is troubleshooting a new GRE over IPsec tunnel. The tunnel is established but the engineer cannot ping from spoke 1 to spoke 2. Which type of traffic is being blocked?
- A. ISAKMP packets from spoke2 to spoke1
- B. ESP packets from spoke1 to spoke2
- C. ESP packets from spoke2 to spoke1
- D. ISAKMP packets from spoke1 to spoke2
Answer: C
NEW QUESTION # 57
An engineer must configure remote desktop connectivity for offsite admins via clientless SSL VPN, configured on a Cisco ASA to Windows Vista workstations. Which two configurations provide the requested access? (Choose two.)
- A. Citrix bookmark via the ICA plugin
- B. SSH bookmark via the SSH plugin
- C. RDP2 bookmark via the RDP2 plugin
- D. Telnet bookmark via the Telnet plugin
- E. VNC bookmark via the VNC plugin
Answer: C,E
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa98/configuration/vpn/asa-98-vpn-config/webvpn-configure-gateway.html
NEW QUESTION # 58
Refer to the exhibit. What is a result of this configuration?
- A. Spoke 1 fails the authentication because the authentication methods are incorrect.
- B. Spoke 2 passes the authentication to the hub and successfully proceeds to phase 2.
- C. Spoke 2 fails the authentication because the remote authentication method is incorrect.
- D. Spoke 1 passes the authentication to the hub and successfully proceeds to phase 2.
Answer: A
Explanation:
Auth local on HUB must match auth remote on SPOKE.
NEW QUESTION # 59
The corporate network security policy requires that all internet and network traffic must be tunneled to the corporate office. Remote workers have been provided with printers to use locally at home while they are remotely connected to the corporate network. Which two steps must be executed to allow printing to the local printers? (Choose two.)
- A. Add a persistent static route in the client OS for the local LAN network.
- B. Check the Allow Local LAN access checkbox in the Cisco AnyConnect client.
- C. Configure the split-tunnel-policy on the Cisco ASA to tunnelspecified.
- D. Configure the split-tunnel-policy on the Cisco ASA to excludespecified.
- E. Configure the split-tunnel-policy on the Cisco ASA to tunnelall.
Answer: B,D
Explanation:
https://www.cisco.com/c/en/us/support/docs/security/asa-5500-x-series-next-generation-firewalls/70847-local-lan-pix-asa.html
NEW QUESTION # 60
......
Free Exam Files Downloaded Instantly: https://www.practicedump.com/300-730_actualtests.html
300-730 Free Exam Questions with Quality Guaranteed: https://drive.google.com/open?id=1UKlQGM34uhESle9FJNY0btgwQ1EPXCQ-